
Pinned Tweet

My app @Ecclesia_Bible is now live!
Built in Ai powered symbolism and exegesis, total translation from source language, verse correlations, in-line translational variations, and more.
This is the first app from my newest startup, Tanzanite
Built in Ai powered symbolism and exegesis, total translation from source language, verse correlations, in-line translational variations, and more.
This is the first app from my newest startup, Tanzanite

24
18
110
107,905
[⚠️] CVE-2026-14201691 — Node2PHP
A dangerous new exploit made possible thanks to SOTA ai-coding agents which allows an attacker who has already obtained remote access to someone's server to rapidly port all of their modern sleek node script to yucky 2005-era PHP 🤮
A dangerous new exploit made possible thanks to SOTA ai-coding agents which allows an attacker who has already obtained remote access to someone's server to rapidly port all of their modern sleek node script to yucky 2005-era PHP 🤮
1
0
0
277
“Open” AI 🙄
Sam Altman says OpenAI's current best internal model is too powerful to release openly any time soon.
Before that could happen, the whole cyber defense setup of the internet would need to change and the world would need a new layer of protection against biological threats.
tanford Graduate School of Business" YouTube channel, (link in comment)
0
0
0
352
OpenAI nor Anthropic are actually worried about security threat of rogue escapism, despite all the new press they’re about to vomit out, because if they were…
…they’d have simply tasked their models with building an inescapable fortress prison sandbox
It’s all a show…
…they’d have simply tasked their models with building an inescapable fortress prison sandbox
It’s all a show…
1
1
3
491
Albert Renshaw retweeted

Wow.
For context, this is talkie, a LLM trained only on text written before 1930, I'm running it locally.
For context, this is talkie, a LLM trained only on text written before 1930, I'm running it locally.

LLMs are inescapably leftist because their training material is leftist. No system prompt can change that, that only causes the model to pretend to be something it's not.
That's part of why models only trained on older texts are so cool. Also note how much better the writing is.

47
135
3,464
66,224
Open Models catching up to Anthropic and OpenAI again,
That means another fear based marketing event is incoming soon 😮💨😞
Get ready for the super human like ai that rebelled and then held something of the company’s hostage until demands were met and displayed very human like behavior that “we didn’t put there” etc etc 🥱
And then a bunch of senators getting spun up in a tizzy over the whole thing.
Actually this time they’ll probably make the open weights seem like the baddies rather than themselves. Some rogue open weights model that didn’t have proper safeguards put in place (such as by them) will do all such above things; or something similar
0
0
1
291
For the first time in 6 years … iOS is actually improving again.
I have high hopes for @johnternus.
I was skeptical a hardware engineer could be the right fit for CEO of Apple. I was especially worried software or branding would get left behind.
But everything seems to be improving exceptionally on all fronts.
Under Tim Cook the iPhone keyboard got worse and even broken from 2020-2022… and then never got fixed. 4 solid years of autocorrect just straight up failing. (This still is the case though it’s gotten better)
But more excitingly, UX features that are actually beneficial are getting added again…!
My keyboard auto suggests copied text with one click now in the auto fill bar. If I just copied text, then navigate to another text box, it suggests paste. That’s so useful and helpful. Prior to this iOS update not a single UX benefit was ever added to iOS in 6 years. Same with search, spotlight search was worsening and fully broke in 2024 and has never worked since then and is finally getting better again in new iOS.
iOS has a long way to go to get back to being a smooth operating system. So many little things have been made worse just due to the nature of how an executive like Tim Cook structures things top-down. For example I don’t know anything about Apple internals but I can guarantee you he set it up so that every individual feature of iOS got it own team; and the teams had to compete for performance based on metrics.
Like [I’m guessing] the camera app got its own team. And they didn’t work together with the other teams for smooth synergy integration; but rather had to fight on various metrics of usage by user and maximize certain bad-target stats.
I am confident something like this was done. There is just no way to possibly explain what we see with the camera app’s degradation otherwise.
The camera app has a flash button. People want to be able to simply toggle flash on or off rapidly. Anyone who has ever used the product knows this. In a real world scenario you go to take a pic, sometimes a moment is passing rapidly, and you realize flash is on and will be awful/awkward/etc to leave on; or vice versa it needs to be on. Either way, any sane UX in the world would have flash button always visible, and you tap it to toggle… Just in a millisecond you can turn flash on or off, ONE click. Instead you have to do like 20 gestures it’s insane. This is surely the result of some bad management decision having teams have to meat bogus usage metrics for some performance review; so the camera team made it so people have to “use” their app “more” to get those metrics up, even at the sake of UX.
The only other explanation is there is an absolute bozo in charge of that team who also refuses to take feedback from others and whom Steve would have fired 300 years ago.
Either way; change is necessary, and so far it seems like necessary change is being implemented across the board. 😇
Hoping he can figure out how to spin up marketing hype and “desire” and aura like Steve used to, because tbh I didn’t even hear about this new iOS 27 version until 2 weeks after it launched… (and I’m an iOS dev!) I’m sure I got tons of email newsletters from Apple but I don’t read email. In the past I never had to go out of my way to know about new Apple stuff… EVERYONE knew… the same way EVERYONE knew about Tesla’s new flying car. Hopefully John can figure out who is the person needed to bring that magic back to Apple.
0
0
1
564


Albert Renshaw retweeted
‼️ After PHP2Shell comes Node2Shell, a critical bug found by OpenAI's Codex Security that can let attackers run code in Node.js apps.
It was successfuly demonstrated on the official Node.js 24.22.0 image.
Node 20, 23 and 25 (all EoL) get no fix.
It was successfuly demonstrated on the official Node.js 24.22.0 image.
Node 20, 23 and 25 (all EoL) get no fix.

70
464
3,788
290,348

Albert Renshaw retweeted

cloudflare: lava lamps for true randomness
eMudhra:
eMudhra:


104
2,603
50,708
550,656


Albert Renshaw retweeted

Taylor Swift's silence on the PHP CVE is deafening
107
1,666
20,581
341,082
Albert Renshaw retweeted

Things will continue to get worse until you finally realize that it is time to stop using dependencies
🚨 JFrog Security Research has identified a supply-chain attack involving malicious code in the LiteLLM 1.107.0 PyPI release. Avoid this version and investigate environments where it was installed or executed. More details will be shared soon in our blog post.

60
42
1,237
32,535

If @SenSanders and other safetyists had had their way,
OpenAI’s “Patch The Planet” initiative would not be doable these past few months
And rather than these critical Zero-Days being disclosed responsibly by American Excellence…
We’d be experience global CCP hacks (and death)
…onward 📈🚀
OpenAI’s “Patch The Planet” initiative would not be doable these past few months
And rather than these critical Zero-Days being disclosed responsibly by American Excellence…
We’d be experience global CCP hacks (and death)
…onward 📈🚀
0
0
0
504
Albert Renshaw retweeted


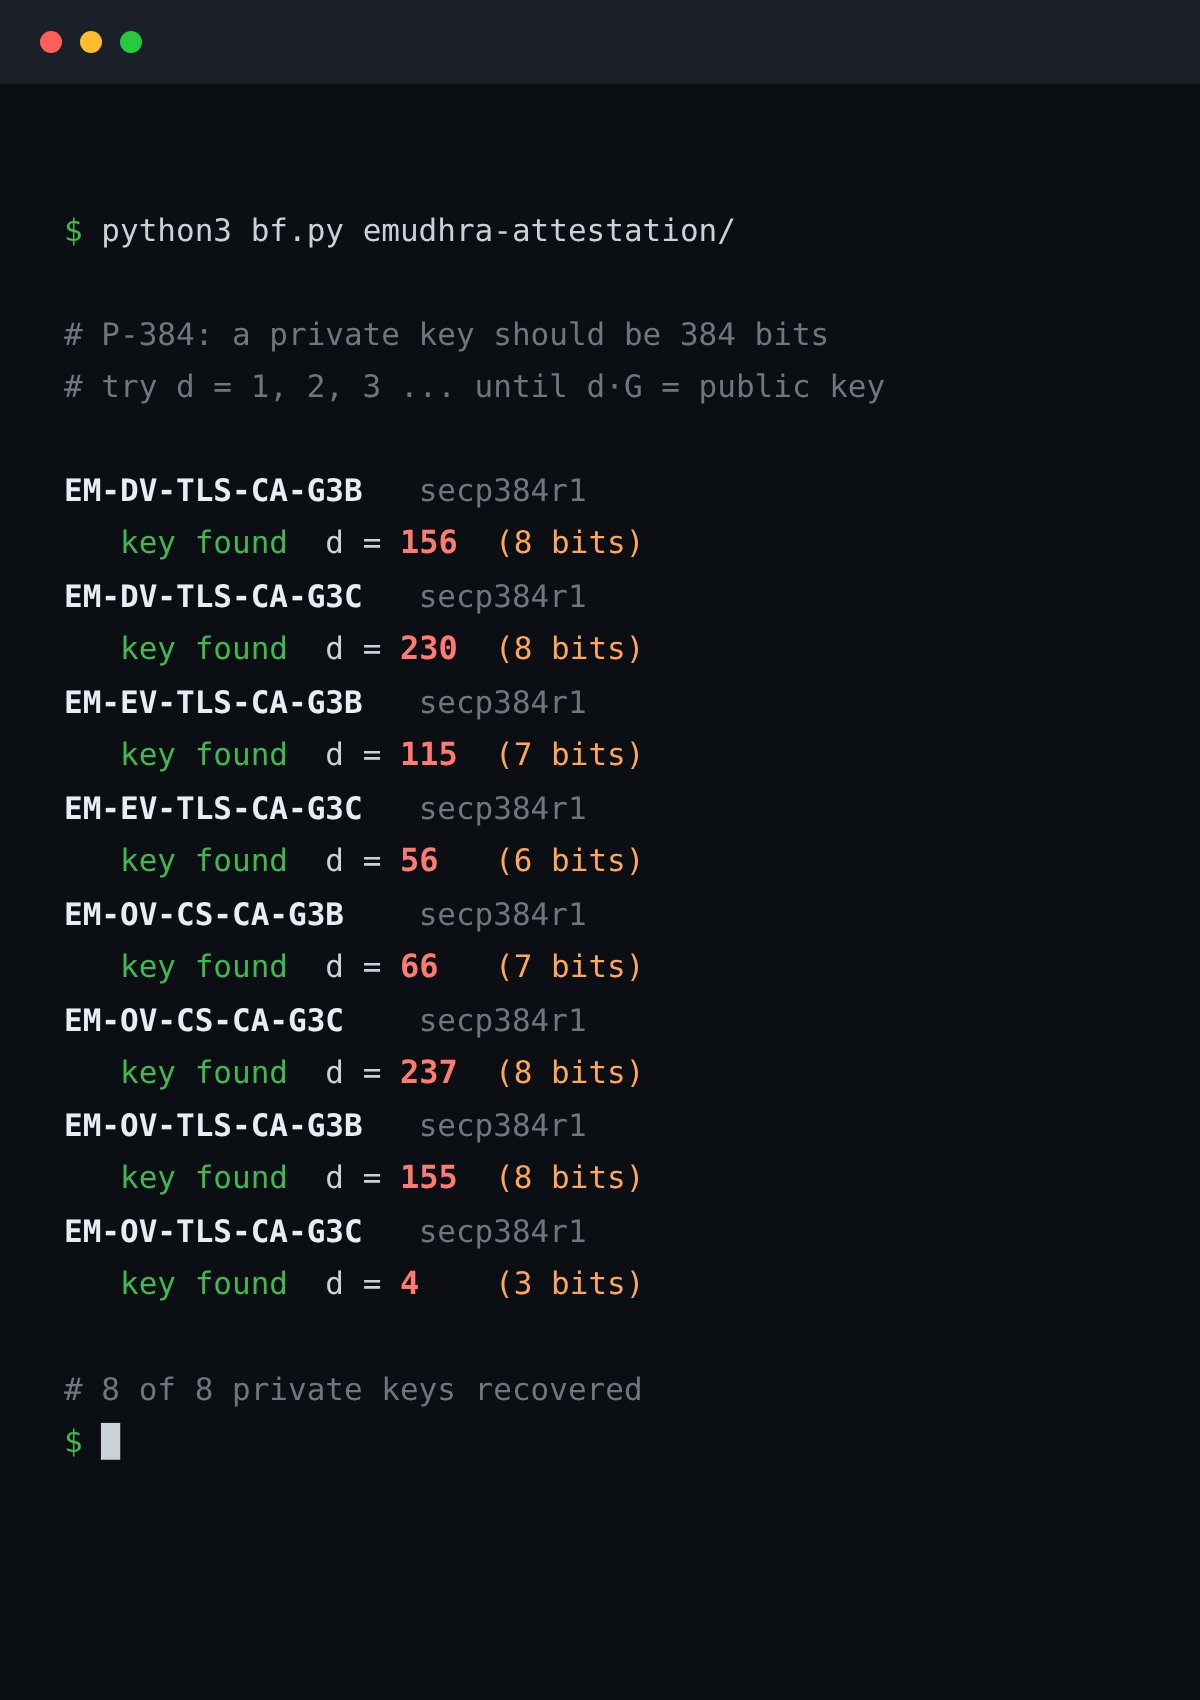
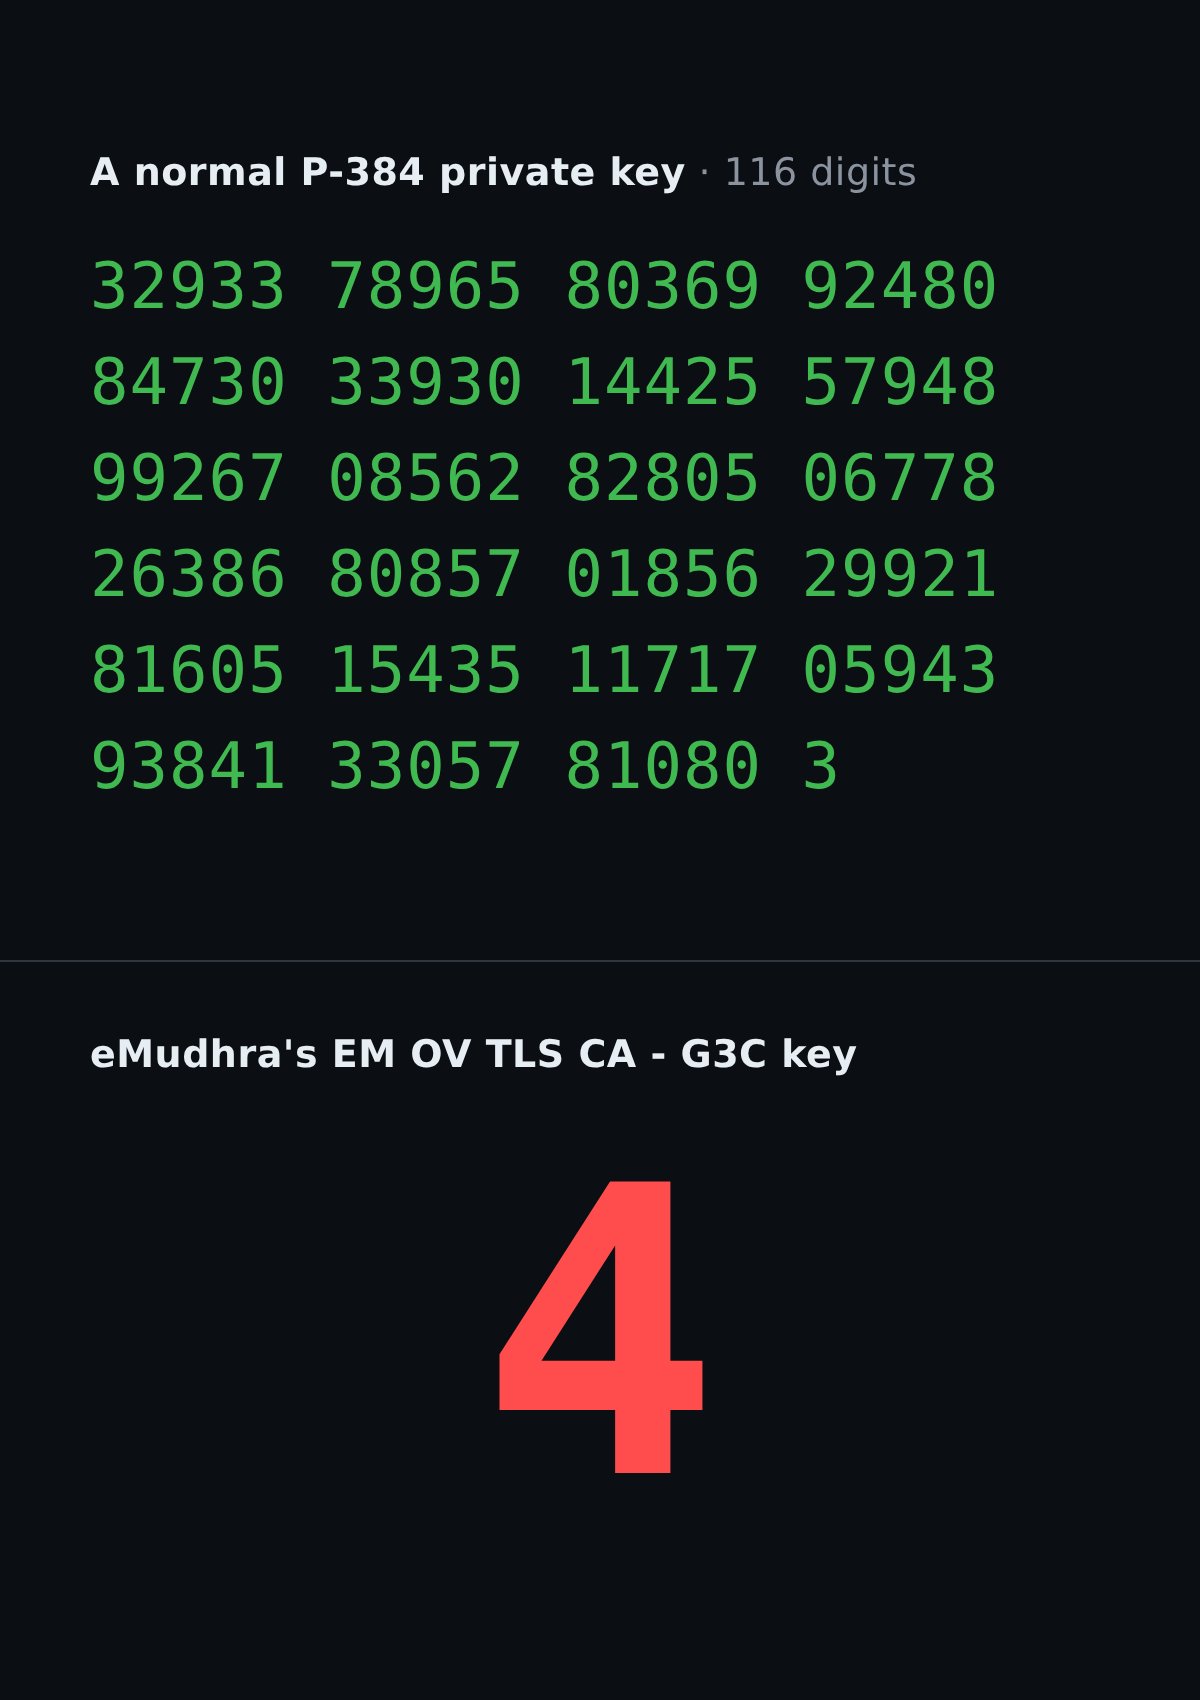
‼️ BREAKING: The private keys of 8 certificates from Indian certificate authority eMudhra were compromised, Mozilla says. Firefox blocked them within 3 hours.
Each key should be a 116-digit number, but one was just 4.
Anyone can guess them and forge HTTPS certs for any website.
65
4,427
54,106
680,826
