

Seeing a few posts today saying Anthropic just open sourced the Claude Code sandbox. It's been on GitHub for about a year, and the latest release was all Windows changes.
Worth a look anyway if you run agents or local MCP servers on your own machine. It wraps any process and limits which files and hosts it can reach, and you don't need a container for it.
Worth a look anyway if you run agents or local MCP servers on your own machine. It wraps any process and limits which files and hosts it can reach, and you don't need a container for it.
2
1
2
245

Attackers were never going to ask Claude nicely. They've already got open models with no filters.
A block like this mostly hits defenders checking their own gear. @AnthropicAI hasn't said anything yet, so I'm hoping it's a twitchy classifier and not an actual policy..
A block like this mostly hits defenders checking their own gear. @AnthropicAI hasn't said anything yet, so I'm hoping it's a twitchy classifier and not an actual policy..
Claude can no longer “Reverse Engineer Anything.”
Anthropic just quietly killed REA.
But Interesting timing.
After a few viral cases of people using Claude to reverse-engineer Samsung TV firmware and identify data-collection services, Anthropic appears to have restricted those lities.


0
0
0
255
Before anyone turns elicitations on at work, have a look at which MCP servers you've actually got connected.
One dodgy server that can pop a form up inside Claude asking for details is a pretty good phishing setup. Claude should be showing which server is asking every time.
One dodgy server that can pop a form up inside Claude asking for details is a pretty good phishing setup. Claude should be showing which server is asking every time.
We’re adding support for MCP Tasks and Elicitations in Claude.
Tasks let Claude give plugins long-running jobs such as deep research and report back when they’re done.

4
0
8
318
I used to work at an MSP with around 300 clients, mostly on FortiGates. Every customer has their own change window and their own idea of when downtime is okay, so an edge patch takes a lot longer in the real world to roll out than the advisory makes it sound.
I imagine there will soon be more firewalls in an HA pair so they can be patched one node at a time immediately without users noticing. A lot of edge boxes stay unpatched because the update means downtime.
I imagine there will soon be more firewalls in an HA pair so they can be patched one node at a time immediately without users noticing. A lot of edge boxes stay unpatched because the update means downtime.
🚨 Exposed infrastructure reveals how ransomware affiliates used AI to hack networks and steal data.
8,257 messages. 133 AI sessions. 62 organizations targeted.
Operators exploited Fortinet, SimpleHelp, and cPanel flaws.
Inside the operation ↓ thehackernews.com/2026/10/expose…
1
0
4
202
Cheaper per token doesn't count for much if the model thinks longer to make up for it.
If you're picking a model for agents, cost per finished task is what should decide it, and that's barely moved here on @Kimi_Moonshot
If you're picking a model for agents, cost per finished task is what should decide it, and that's barely moved here on @Kimi_Moonshot
Kimi K3.1 Pro launches at 4th on the Artificial Analysis Intelligence Index scoring 55, making large gains in agentic performance; it will be the leading open-weights model once its weights are published
@Kimi_Moonshot's new reasoning model gains 11 points over Kimi K3 (max, ude Opus 5.5 (max with fallback, 58), Claude Sonnet 5.5 (max with fallback, 56), and Muse Wonder Full (max, 56) on the Intelligence Index.
Once the weights for K3.1 Pro are released it will be the highest-scoring open weights model and the gap between the leading open weights and proprietary models on the Intelligence Index will narrow from 12 points to 3.
Key results:
➤ Large gains in agentic performance: Kimi K3.1 Pro scores 3rd on GDPval-AA with 1,846 Elo, up 312 Elo from Kimi K3, behind only Claude Opus 5.5 (1,866 Elo) and Muse Wonder Full (1,857 Elo). Kimi K3.1 Pro also achieves the highest score of any model on Terminal-Bench 4.0. K3.1 Pro scores 67%, up from 13% for Kimi K3 and ahead of Claude Sonnet 5.5 (64%). AutomationBench-AA, which tests agentic SaaS workflows, rises from 58% to 73%.
➤ Gains in other evals are more moderate: Humanity's Last Exam rises from 47% to 52%, CritPt from 23% to 25%, and SciCode from 59% to 61%. AA-Omniscience Index rises from 20 to 30, as the hallucination rate falls from 53% to 44% and accuracy rises from 48% to 51%.
➤ Cost per Task roughly equal to Kimi K3 at $1.98 per Task: K3.1 Pro uses 55K output tokens per Intelligence Index task, 14% more than Kimi K3 at 48K, while its first-party token prices are 33% lower.
Additional model details:
➤ Context window: 1M tokens.
➤ Size: 2.8T total, 104B active parameters
➤ Input modalities: Text and image
➤ Weights and license: Weights currently not published, Moonshot is expected to release the weights soon after launch
➤ Pricing: $2/$10/$0.20 per 1M input/output/cache hit tokens, 33% lower than Kimi K3 on all three rates.
Congratulations to the team at @Kimi_Moonshot on the release!


0
0
2
176
More subnets should be chasing paying customers like this instead of just emissions | $TAO
From my testing, Lium was easy to get going because it was built for agents from the start, with API keys, budget caps and docs my agent could read on its own.
I'm thinking of starting a real-use subnet review series where the very first check will be how agent friendly it is. If my agent is given your website URL and it doesn't immediately how to do everything, its a fail.
Lium now hosts over $30m worth of hardware.
including 225 B300s.
91% of our supply is rented.
lium is the only platform in the world making these GPUs both accessible and affordable.

1
0
17
612
If you're running agents at work, this is a decent template to copy.
Get an external party who didn't build your monitoring to spend a few weeks trying to get around it. Whoever set it up is going to have the same blind spots when they test it.
That's just common sense.
Get an external party who didn't build your monitoring to spend a few weeks trying to get around it. Whoever set it up is going to have the same blind spots when they test it.
That's just common sense.
Two employees from METR and Redwood Research worked on premises at OpenAI for three weeks this summer in an embedded assessment pilot. This team evaluated the systems OpenAI was using to monitor for misalignment from internal agents. A brief write-up of their work is now public.
0
0
0
189
Banks already let accounting apps in with limited access through bank feeds and APIs. Agents should come in the same way, with their own login, instead of sitting inside the customer's session.
Then the bank can see it's an agent, check what it's allowed to do, and switch that one agent off without locking the person out.
Agents like Grok @bot has its own virtual desktop so you can connect it straight in a browser using your credentials. It gets the full desktop UX.
Then the bank can see it's an agent, check what it's allowed to do, and switch that one agent off without locking the person out.
Agents like Grok @bot has its own virtual desktop so you can connect it straight in a browser using your credentials. It gets the full desktop UX.
SCOOP: Major U.S. banks are detecting unauthorized third-party AI agents inside customer accounts, including some attempting to take actions that appear to be independent of user instructions, sources told Axios.
The findings have alarmed banking executives, who are racing to restrict access to their systems as AI moves at a velocity faster than financial institutions can respond, multiple industry and bank executives told Axios.
Several banks are now preparing for worst-case and even “day after” scenarios, including how to rapidly secure or restore customer accounts if things go wrong, the people said.
Several bank executives told Axios they're struggling to distinguish between human users and AI agents. One executive said banks also struggle to determine whether agents are authorized by customers or potentially operating without their permission, more akin to rogue agent behavior.
Read my latest for Axios here: axios.com/2026/10/22/ai-…
0
0
2
202
DeepSeek got this far on a fraction of what the US labs spend, and gave most of it away as open weights.
This type of capital will be huge. What I'd want to know is whether the open releases keep coming, or whether money this big brings the same pressure to close things up that hit everyone else.
This type of capital will be huge. What I'd want to know is whether the open releases keep coming, or whether money this big brings the same pressure to close things up that hit everyone else.
The Whale has raised another $15 billion.


1
0
5
307

With Claude Duet out, pretty much every big lab has an agent that keeps working while you're away.
I have spent the last few weeks setting up Grokbot and I'm about 7 agents in now including the orchestrator one that I built.
Duet is US only it seems but I have added myself to the waitlist here to see if it can replace it.
I have spent the last few weeks setting up Grokbot and I'm about 7 agents in now including the orchestrator one that I built.
Duet is US only it seems but I have added myself to the waitlist here to see if it can replace it.
We’re opening a research preview of Claude Duet, a new app where Claude works as a proactive agent.
It comes to you with what needs your attention, completes tasks you ask of it, keeps working when you step away, and checks with you before it acts on your behalf.

1
0
1
249

AI finding a PHP bug this big before attackers did is the good version of this story.
The same models can be pointed at every other popular open-source project, and not everyone using them will disclose. Maintainers are going to need a lot more help than they're getting.
The same models can be pointed at every other popular open-source project, and not everyone using them will disclose. Maintainers are going to need a lot more help than they're getting.
OpenAI models helped researchers—operating as part of our Patch the Planet initiative—discover critical security flaws in PHP, an open-source programming language used to run an estimated 70% of websites.
Over the past two months, we led a coalition of maintainers, researchers, and security providers to prepare fixes and protections ahead of disclosure. This duration was necessary because the fix was quite intricate and required a major change to the PHP engine. Every site using PHP can now safely upgrade their version to stay secure, in addition to applying mitigations from various security vendors.
Due to the severity of these flaws and PHP’s widespread use, we consider this bug to be one of the most impactful vulnerabilities in recent memory. It also marks a new phase, where AI can find security bugs with internet-scale impact.
This is an example of the Defender’s Window in action: to our knowledge, frontier AI was able to find this vulnerability ahead of attackers, giving defenders time to prepare.
openai.com/index/coordina…Community noteWiz Research wasn't the first one to discover the exploit. An independent researcher first discovered it: x.com/calif_io/statu…

0
0
0
199
Agree with this. Power gets the headlines because it's the easiest part to point at.
Bringing compute online fast means land, grid connection, cooling, networking and the people to run it all landing at once. One slip-up and the rest wait.
Probably also why some of the neoclouds that got rushed out are so hit and miss.
Bringing compute online fast means land, grid connection, cooling, networking and the people to run it all landing at once. One slip-up and the rest wait.
Probably also why some of the neoclouds that got rushed out are so hit and miss.
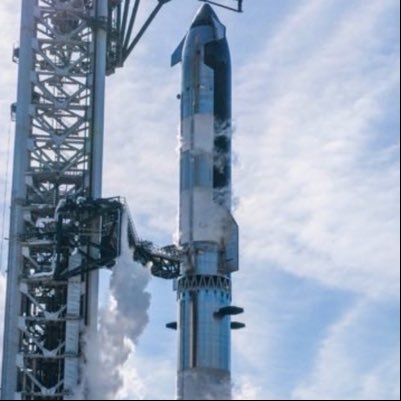
“Lack of electricity” is an oversimplification. Everything is hard about bringing massive compute online at extremely high speed.
If there was twice as much time, this would be relatively easy, but there is not.
0
0
0
128
This is the kind of Claude news I'd like to see more of. Not another benchmark, an early step on a problem where treatment is expensive and often hard to get.
"Early step" is carrying a lot in that sentence though. Keen to see what happens to these designs from here. Well done @AnthropicAI 🫡
"Early step" is carrying a lot in that sentence though. Keen to see what happens to these designs from here. Well done @AnthropicAI 🫡
New on our Science Blog: designing protein binders against scorpion neurotoxins.
Scorpions sting about 1.2m people every year, and antivenoms are often costly or in short supply. Claude has made an early step toward finding new treatments.
anthropic.com/research/claud…

0
0
0
173
The very first owners to use this mostly went straight to the maximum owner cut, within hours of it going live.
That's allowed, and some teams might need it, but the split is now part of the subnet DD. Check it before you stake, and watch what owners ship with the extra | $TAO
That's allowed, and some teams might need it, but the split is now part of the subnet DD. Check it before you stake, and watch what owners ship with the extra | $TAO
Introducing eTAO: a new system giving subnets control over their alpha emission split.
Subnet owners can now decide how much goes to miners, validators, and themselves, based on the specific needs of their subnet.

1
0
7
560
Within about 90 minutes of eTAO going live, five subnets changed their emission split.
Four of them went straight to the 33% owner max, and these should not be surprising:
Consted [SN103]
Consted 2.0 [SN70]
Epago [SN36]
Logic [SN35]
@CookingTao_ [SN122] did the opposite. Owner cut stayed at 18%, validators dropped and miners went up to 64%.
Changes are rate limited to once a week, so these splits stay put for at least a week | $TAO
I like eTAO. A compute subnet and a research subnet shouldn't have to pay out the same way, and now they don't have to | $TAO
It does move some risk onto alpha holders though. Root is paid first, so stakers keep their share whatever the owner picks. The validator slot, where es from, is the one an owner can cut.
Changes are rate limited, so it can't swing overnight. I'd still add it to the checklist: what's the split, when did it last change, and did the owner's own cut go up or down.

5
0
39
3,188