
Pinned Tweet
You can now jailbreak your AMD CPU! 🔥We've just released a full microcode toolchain, with source code and tutorials. bughunters.google.com/blog/542484235…
42
523
1,740
185,388
I have a (dumb) theory about Intel. They used to ship beautiful printed manuals anywhere in the world for free if you called them. That program made a lot of engineering students customers for life. Then some middle manager killed it, and probably got a promotion.
These are forever gone btw. Intel stickers had cool semiconductor holographics on the backside that no one will ever see, it wasn't there by accident. It was too beautiful for the modern marketing bug people, so they wiped it out.


135
2,215
45,699
1,298,152
Hey... quick question, why are anime catgirls blocking my access to the Linux kernel? 😸
lock.cmpxchg8b.com/anubis.html
lock.cmpxchg8b.com/anubis.html

89
136
3,507
208,916

Tavis Ormandy retweeted
EntrySign was nominated for two Pwnies (best crypto bug and best desktop bug)! 🥳
youtube.com/live/TuKPA-CeD…
@__spq__ @sirdarckcat @taviso
youtube.com/live/TuKPA-CeD…
@__spq__ @sirdarckcat @taviso
0
6
42
16,181
This is neat, using EntrySign to backport microcode patches to EOL systems without BIOS updates. github.com/divestedcg/rea…
3
22
68
17,586
I just learned that OSC8 (hyperlinks) in Windows Terminal uses ShellExecute(). Excellent trolling potential for README files 😆

12
83
461
55,936
Tavis Ormandy retweeted

Back in 2023, the assessment of the pre-authentication vulnerability in SSH was that it wasn't exploitable on Linux.
For my OffensiveCon 2025 keynote, I wrote enough of an exploit to show, with the right heap groom and stabilization, it's likely exploitable. Then I tried to have AI do it.
Up to @taviso whether that merits switching to Windows 98 :)
youtube.com/watch?v=Y1naY3…
For my OffensiveCon 2025 keynote, I wrote enough of an exploit to show, with the right heap groom and stabilization, it's likely exploitable. Then I tried to have AI do it.
Up to @taviso whether that merits switching to Windows 98 :)
youtube.com/watch?v=Y1naY3…
If someone get a working OpenSSH exploit from this bug, I'm switching my main desktop to Windows 98 😂 (this bug was discovered by a Windows 98 user who noticed sshd was crashing when trying to login to a Linux server!)
4
34
242
52,811
Tavis Ormandy retweeted
The recording of our OffensiveCon presentation about EntrySign is live! youtu.be/sUFDKTaCQEk
Slides at entrysign.top
@sirdarckcat @__spq__
Slides at entrysign.top
@sirdarckcat @__spq__
2
21
101
33,738
Tavis Ormandy retweeted

Fuzzing Windows Defender in the Honggfuzz+IntelPT (hardware) mode
scrapco.de/blog/fuzzing-w…
by @buherator
scrapco.de/blog/fuzzing-w…
by @buherator
1
61
193
18,725
The code and tutorials are here if the link doesn't work! 😒 github.com/google/securit…
3
21
137
18,983
welp, it looks like an OEM leaked the patch for "AMD Microcode Signature Verification Vulnerability" 🔥 The patch is not in linux-firmware, so this is the only patch available😡

5
56
284
42,371
Tavis Ormandy retweeted

Hey! I made a game in Bash with raylib! It's a "bullet hell" game featuring beloved penguin Tux vs an evil mutant Window!
Bash is a simple scripting language, so simple it doesn't have floating point variables/arithmetic! So how was this game possible? 👇
Bash is a simple scripting language, so simple it doesn't have floating point variables/arithmetic! So how was this game possible? 👇
11
46
298
38,713
Tavis Ormandy retweeted

Intel HW is too complex to be absolutely secure! After years of research we finally extracted Intel SGX Fuse Key0, AKA Root Provisioning Key. Together with FK1 or Root Sealing Key (also compromised), it represents Root of Trust for SGX. Here's the key from a genuine Intel CPU😀

100
933
4,807
974,314
Tavis Ormandy retweeted

@CrowdStrike This 100% matches our/@taviso's conclusions derived from analyzing the crash report/disasm 🧠
RAX: input pointer array
R11: index (0x14/20d)
Accessing Array[20] retrieved the 21st item (as arrays are 0-based). This returned an invalid memory address that 💥'd when deref'd!
RAX: input pointer array
R11: index (0x14/20d)
Accessing Array[20] retrieved the 21st item (as arrays are 0-based). This returned an invalid memory address that 💥'd when deref'd!

4
23
67
26,287
Tavis Ormandy retweeted

This morning, we published the Root Cause Analysis (RCA) detailing the findings, mitigations and technical details of the July 19, 2024, Channel File 291 incident. We apologize unreservedly and will use the lessons learned from this incident to become more resilient and better serve our customers. To any customer still affected, please know we will not rest until all systems are restored.
For the executive summary and full RCA, please visit crowdstrike.com/falcon-content…
For the executive summary and full RCA, please visit crowdstrike.com/falcon-content…
133
453
1,405
455,363
I wasted a bunch of time trying to figure out why xterm starts so slowly on Windows... and solved it with a dumb LD_PRELOAD hack 😆 lock.cmpxchg8b.com/slowterm.html
9
46
200
32,698
Tavis Ormandy retweeted
No surprises here, but @CrowdStrike confirms @taviso's analysis, that the bug was indeed not due to a NULL-pointer deference 🧠 ...but rather "an out-of-bounds memory read"

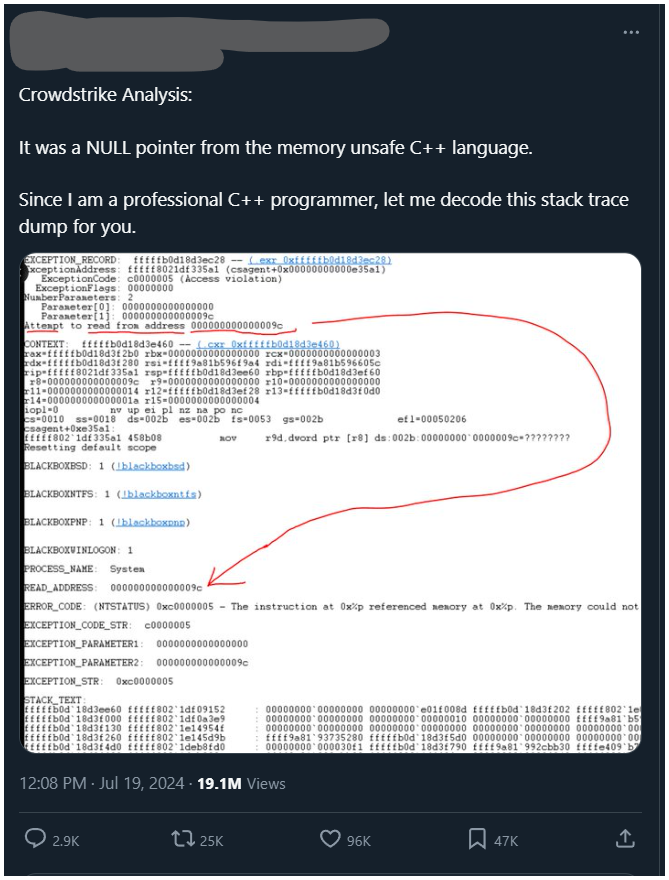
This strange tweet got >25k retweets. The author sounds confident, and he uses lots of hex and jargon. There are red flags though... like what's up with the DEI stuff, and who says "stack trace dump"? Let's take a closer look... 🧵1/n
20
232
1,160
167,336
This strange tweet got >25k retweets. The author sounds confident, and he uses lots of hex and jargon. There are red flags though... like what's up with the DEI stuff, and who says "stack trace dump"? Let's take a closer look... 🧵1/n
241
2,986
15,100
3,277,646
Here is the same crash seen by Patrick, except he saw the entry 0xffff9c8e00000008a, nowhere near NULL! If this is uninitialized data, perhaps it was okay during testing and that's why CS didn't catch it 🤷♂️ 8/n
x.com/patrickwardle/…
x.com/patrickwardle/…
I don't do Windows but here are some (initial) details about why the CrowdStrike's CSAgent.sys crashed
Faulting inst: mov r9d, [r8]
R8: unmapped address
...taken from an array of pointers (held in RAX), index RDX (0x14 * 0x8) holds the invalid memory address
@_JohnHammond


10
82
1,950
398,705