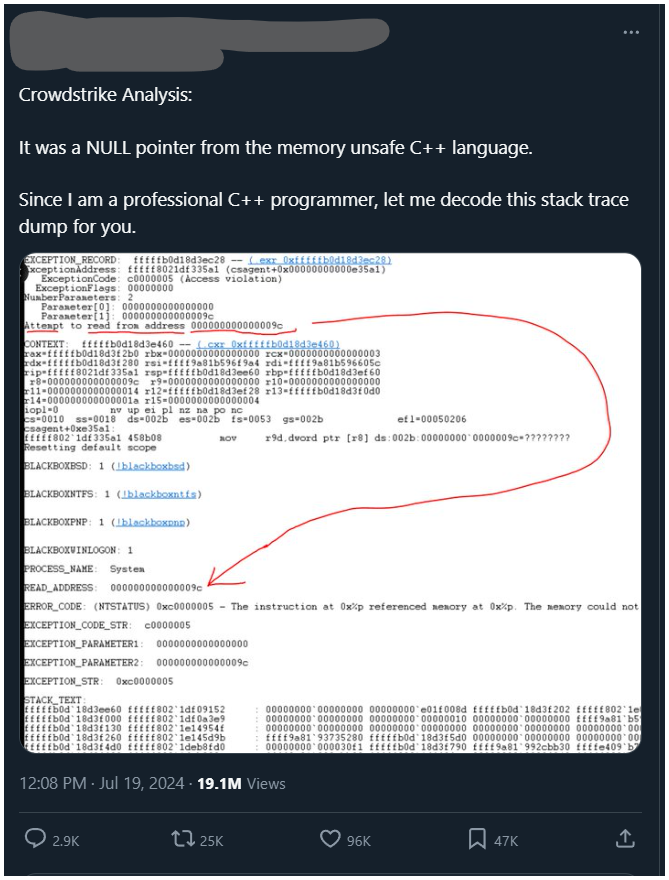
This strange tweet got >25k retweets. The author sounds confident, and he uses lots of hex and jargon. There are red flags though... like what's up with the DEI stuff, and who says "stack trace dump"? Let's take a closer look... 🧵1/n
Jul 20, 2024 · 8:40 PM UTC
241
2,986
15,101
3,277,646
This is actually a screenshot of !analyze -v output, I think the author conflated "stack trace" and "minidump". Regardless, he only looks at the decoded exception record and concludes "it was a NULL pointer"...? 🤔 2/n
5
37
1,979
282,326
It is a plausible explanation, 0x9c is not NULL, but dereferencing near-NULL addresses can have the same root cause. He explains that the code was reading a field at offset 156 from a NULL object pointer. 3/n

8
26
1,494
277,761
Well, except... we can see in his screenshot that MSVC generated mov r9d, [r8]? That's really odd... I spend half my life looking at MSVC output, and I would expect to see mov r9d, [r8+0x9c], so what's up with that? 4/n

8
28
1,604
262,617
Maybe I'm wrong, let's test it in godbolt godbolt.org/z/sdz4PGxxo. Nope, the code doesn't match! The code is either more complicated, or his hypothesis is incorrect. There is a way to check, he could type `u` (unassemble) into kd and examine the surrounding code. 5/n

5
33
1,581
246,021
He didn't, but we still can! His version of the faulting module has the bytes 45 8b 08 at csagent+0xe35a1, I found that version in VT, and had a look. In fact, there *is* a NULL check (test r8, r8; jz) immediately before the dereference, so his theory is provably *wrong* 🛑 6/n

9
94
2,255
262,697
This code is reading pointers from a table in a loop, and some are invalid. Perhaps an error parsing a configuration file left some entries uninitialized, and one just happened to be 0x9c? It's just a theory, but at least mine fits the facts😆 7/n
11
39
1,741
226,087
Here is the same crash seen by Patrick, except he saw the entry 0xffff9c8e00000008a, nowhere near NULL! If this is uninitialized data, perhaps it was okay during testing and that's why CS didn't catch it 🤷♂️ 8/n
x.com/patrickwardle/…
x.com/patrickwardle/…
I don't do Windows but here are some (initial) details about why the CrowdStrike's CSAgent.sys crashed
Faulting inst: mov r9d, [r8]
R8: unmapped address
...taken from an array of pointers (held in RAX), index RDX (0x14 * 0x8) holds the invalid memory address
@_JohnHammond


10
82
1,950
398,705

@taviso If you notice, he also made a mistake in calculating the offset of the structure, where he shifts the first field by 4 bytes, while in reality, the first field has the same address as the structure.
9
7
809
120,952
@twittatore Huh, well spotted. I definitely don't get the impression he spends much time figuring out types in a debugger 😆
5
0
560
109,852

@taviso It's an exception logged somewhere, and it probably contains some form of stack trace, so why it's not a "stack trace dump"? In my understanding "dump" stands for the fact of saving, or maybe the presence of RAM memory data in there🤔
2
0
30
45,412

@taviso ??? But he said really big words and posted images with lots of numbers and letters??
6
2
505
70,046

@taviso Stack trace dump is when you read a stack trace on the toilet.
6
3
385
57,336

@taviso the way I don’t code but knew he was full of shit and just had to wait for someone not-repugnant to shut his bs down lmao
2
0
143
27,383

@taviso He still can't write an exploit on the wall while showering like you can and have, I forget how many times. 😉
1
2
91
51,664
@taviso @andrew_im All I could do was roll my eyes at the guys DEI comment
2
0
75
19,912

@taviso the dig at dei here is truly baffling x.com/miraculous_cak…
people will really be like, "using the Woke rust? that pales in comparison to my strategy, avoiding memory bugs in the apolitical c++" and then neither avoid politics nor memory bugs in c++
1
0
25
5,045

@taviso What’s even the point of trying to analyze this compiled code in memory?
It’s not gonna shed any light on the nature of the mistake that was made.
Without symbols or source, it just seems like a pointless exercise.
It’s not gonna shed any light on the nature of the mistake that was made.
Without symbols or source, it just seems like a pointless exercise.
6
0
10
12,338

@taviso Thanks for speaking out about that guy’s ramblings. The shitting on DEI was bad enough and an obvious red flag so I assumed the rest was bullshit even before I read it
0
0
13
814


@taviso @FSchweitzer He mentions James O‘keefe right in his bio. That’s pretty much all one would have to read to judge his trustworthiness imho.
0
0
4
869


@taviso Yeah that tweet thread made no sense. Glad you tried :-)
0
0
1
942


@taviso You still didn’t address the DEI issue
0
0
0
1,105


@taviso The biggest red flag was: "Oh, it's a null pointer reference. A check for null would have fixed it."
2
0
58
19,323

@taviso Could DEI have caused this kind of sloppiness? This was a failure on multiple levels that I can see. First the poster made a rookie mistake and the people who retweeted didn’t do their jobs in vetting and just rolled it out to their timelines.
3
0
29
6,759

@taviso this might be because its not even his own - he just took some image from twitter and draw some lines on it. original source see:
x.com/snicoara/statu…
x.com/snicoara/statu…
This Crowdstrike issue seems to be an issue with addressing invalid memory space... #Crowdstrike #BSOD


2
1
29
3,398


