Pinned Tweet
FYI:
I'm not engaging on Twitter. It's leadership is undermining saftey and enabling hateful content targeting my 🏳️🌈 and 🏳️⚧️ friends (among others).
But I still want to reach people here, so will be posting basic updates w/ links off-site for discussion.
hachyderm.io/@chandlerc
I'm not engaging on Twitter. It's leadership is undermining saftey and enabling hateful content targeting my 🏳️🌈 and 🏳️⚧️ friends (among others).
But I still want to reach people here, so will be posting basic updates w/ links off-site for discussion.
hachyderm.io/@chandlerc
0
1
48
9,983
Thoughts on predictors.fail over where I regularly post:
hachyderm.io/@chandlerc/113…
(Reminder, I'm not active here, find me on hachyderm or bsky)
hachyderm.io/@chandlerc/113…
(Reminder, I'm not active here, find me on hachyderm or bsky)
0
1
8
1,681
Really excited about what the team has accomplished here! Also, the post shares some really fun details of hardened libc++, huge credit to the #Clang, #LLVM, and libc++ community!
Excited to share our latest post on memory safety! We're tackling spatial safety in our massive C++ codebase by hardening libc++ *by default*. It adds bounds checks to things like std::vector, preventing a fair bit of out-of-bounds vulnerabilities: security.googleblog.com/2024/11/retrof…
0
4
32
3,761
Proud to start sharing Google's strategy for tackling our remaining memory safety challenges: security.googleblog.com/2024/10/safer-…
High level, but it outlines the long-term strategy. We'll be sharing more detailed posts in this series.
#CPlusPlus #RustLang #CarbonLang
High level, but it outlines the long-term strategy. We'll be sharing more detailed posts in this series.
#CPlusPlus #RustLang #CarbonLang
6
12
68
6,892

@chandlerc1024 *chanting in the distance* borrowck, borrowck, borrowck, bor…
1
0
0
80
@static_assert_0 Basically.
There may be some differences, but id generally expect us to have a borrow checker or something equivalent.
There may be some differences, but id generally expect us to have a borrow checker or something equivalent.
1
0
1
93

@chandlerc1024 What's the benefit of Carbon over Rust?
1
0
2
290
@JAldrichPL If it works, much more comprehensive, integrated, and incremental interop and even automated migration where possible.
0
0
4
173
@chandlerc1024 Does Carbon have a solution for safety yet? I seem to remember it was a “safe subset” approach initially right?
1
0
2
205
@static_assert_0 Carbon is still early stages, but we're aiming to have a similar level of safety to Rust or Swift long term.
1
0
4
184
Chandler Carruth retweeted
Excited to share Google's memory safety strategy! We're working to build safer software by migrating to memory-safe languages like Rust as well as hardening our existing C++: security.googleblog.com/2024/10/safer-….
We'll be sharing more details in upcoming posts.
We'll be sharing more details in upcoming posts.
2
69
228
63,235

Would analyzers/sanitizers/debug tools etc. in the C/C++ ecosystem be upset if my code read 1 byte at the end of string views? for any useful data type/source of string view.
(More interested in real world answers than theoretical answers.)
(More interested in real world answers than theoretical answers.)
12
1
18
7,257
@ocornut Yes, ASan and other sanitizers will complain.
You could also get unlucky and have mapped memory end. For example, with a string view of an exact page-sized string, but where it was shrunk to zero length at the end, you could easily have the one byte be on an unmapped page.
You could also get unlucky and have mapped memory end. For example, with a string view of an exact page-sized string, but where it was shrunk to zero length at the end, you could easily have the one byte be on an unmapped page.
0
0
15
5,566
Amazing update to one of my favorite stories about memory safety from Android folks: security.googleblog.com/2024/09/elimin…
Degree to which memory safe languages reduces this category of exploitation, and lower the aggregate exploit severity of a product is remarkable.
hachyderm.io/@chandlerc/113…
Degree to which memory safe languages reduces this category of exploitation, and lower the aggregate exploit severity of a product is remarkable.
hachyderm.io/@chandlerc/113…
0
3
18
2,359
And the fourth amazing edition of the Carbon Copy, your newsletter for #CarbonLang, is out! github.com/carbon-languag…
0
2
21
2,138
Chandler Carruth retweeted
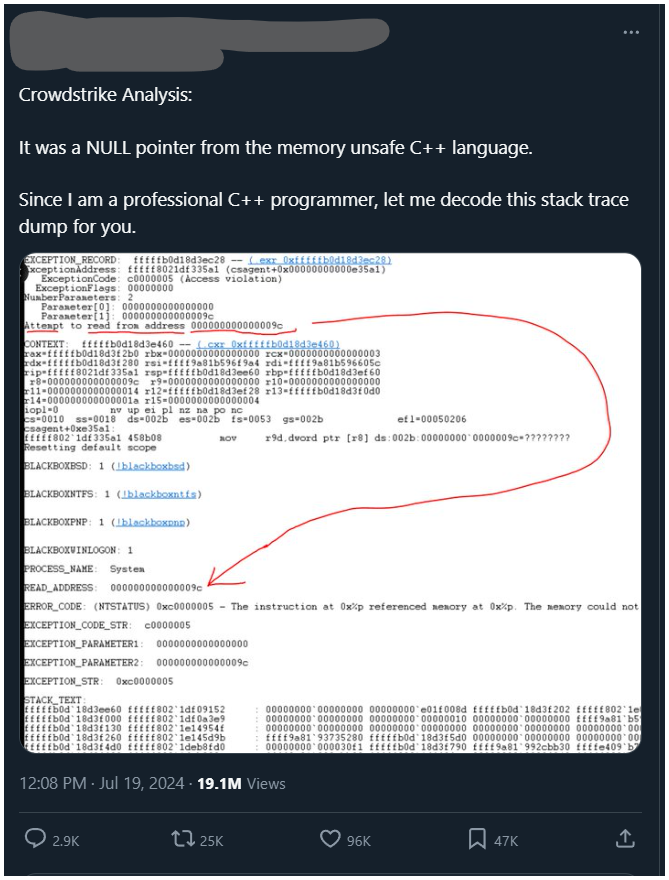
This strange tweet got >25k retweets. The author sounds confident, and he uses lots of hex and jargon. There are red flags though... like what's up with the DEI stuff, and who says "stack trace dump"? Let's take a closer look... 🧵1/n
241
2,986
15,101
3,277,646

🤷♀️ Some people have a fixed ceiling of thought-spend they want to use on their language. If you use things outside of that thought-spend they get frustrated and sad. (We'll ignore that to do similar in C takes either code generation or horrific macros...)
1
8
141
10,136
But some people just want to feel like they know everything about their language. Some people just want to feel like everything is simple and the only complexity is what they themselves introduce to the situation/project. This works great,
until you need to do complex things.
until you need to do complex things.
2
7
117
3,456
@__phantomderp TBH, few of your, or anyone elses PL tweets go as hard as this. +100, well said.
0
0
2
318
Hot off the virtual presses is the 3rd edition of the Carbon Copy!! =D
I'm particularly excited about this one as it digs in a bit deeper into some meaty bits of the language design.
github.com/carbon-languag…
#CarbonLang
I'm particularly excited about this one as it digs in a bit deeper into some meaty bits of the language design.
github.com/carbon-languag…
#CarbonLang
1
2
20
1,938

I was disappointed when I read Carbon wasn't going to try to match Rust on mem safety, but this presentation on lessons learned from and putting their own spin on the Swift/Rust protocol/trait systems has some cool ideas, esp. part 2. Decidable checking!
youtu.be/FKC8WACSMP0?si…
youtu.be/FKC8WACSMP0?si…
2
0
3
1,153
@chandlerc1024 Ah interesting. I think it would he hard add the Rust method of checking after release -- lifetimes and the rules around shared vs mutable borrows and Send/Sync and Cell/RefCell thoroughly permeate all Rust APIs. Maybe the Carbon team is cooking something easier to retrofit tho?
1
0
0
98
@joseph_h_garvin Yeah, adding it afterward makes things harder, no doubt.
But we need to figure out how because we're starting with C++ which is already deeply unsafe, and interop is essential. So harder, but not avoidable IMO.
We have some good ideas tho, including making it a bit less painful
But we need to figure out how because we're starting with C++ which is already deeply unsafe, and interop is essential. So harder, but not avoidable IMO.
We have some good ideas tho, including making it a bit less painful
0
0
2
79
I would like to know how Carbon plans to make sure trait/protocol checking doesn't infinite loop in the presence of variadics though, do my parameter packs always need to stay the same length or shrink too? @chandlerc1024 ?
1
0
0
112
@joseph_h_garvin We definition check variadics with symbolic arity. This also lets us definition check the variadic's arity being valid in all uses of the pack, etc.
The CppNow talk about this should be posted soon, and the proposal for it is under active work: github.com/carbon-languag…
The CppNow talk about this should be posted soon, and the proposal for it is under active work: github.com/carbon-languag…
1
0
1
31

@SeanParent @tvaneerd @zygoloid There are calling conventions that do callee-destruction of by-value parameters, which would make returning a reference to them dangle.
0
0
1
223
Chandler Carruth retweeted
New blog post: Notes from the Carbon panel session at EuroLLVM 2024. muxup.com/2024q2/notes-f…
0
6
20
5,431