
Pinned Tweet

Legend ❤️ makes work less stressful by letting you 🖱️ drag anything anywhere.
Connect multiple Gmail accounts & easily
👨🏾🦱Mention a contact with '+ '
🗂️ Attach a drive file with '/ '
📆 Create a calendar with '! '
Connect multiple Gmail accounts & easily
👨🏾🦱Mention a contact with '+ '
🗂️ Attach a drive file with '/ '
📆 Create a calendar with '! '
Your inbox never stops filling up & ⭐️ 🚩 📧 📥 can only get you so far.

1
3
11
841
Yonatan retweeted

We’re doubling down on open source.
Today we're making PowerSync's entire core open source by moving our remaining source-available (FSL) repos to Apache-2.0
Our hypothesis: less legal friction → more adoption → a stronger business → more investment in open source.
Read 👇
Today we're making PowerSync's entire core open source by moving our remaining source-available (FSL) repos to Apache-2.0
Our hypothesis: less legal friction → more adoption → a stronger business → more investment in open source.
Read 👇
9
13
137
35,928
Yonatan retweeted

#LoFi/42 talk is up! A bit nervous at the start 😄 but here's what we covered:
- Koru's vision and the key decisions behind it: Rust, iroh and CRDTs
- Why local-first matters for data ownership and user experience. Your data lives on your device, you own it, and the app stays fast because it isn't waiting on a server
- Why the future of multi-agent collaboration should be open source and available to everyone
- More videos coming in the next few weeks as I add features to Koru, especially around multiplayer agent collaboration.
Thanks @devYonz for having me!
- Koru's vision and the key decisions behind it: Rust, iroh and CRDTs
- Why local-first matters for data ownership and user experience. Your data lives on your device, you own it, and the app stays fast because it isn't waiting on a server
- Why the future of multi-agent collaboration should be open source and available to everyone
- More videos coming in the next few weeks as I add features to Koru, especially around multiplayer agent collaboration.
Thanks @devYonz for having me!
Thanks @devYonz for organizing and for having me! Looking forward to talking Rust, iroh and CRDTs on Tuesday, and sharing Koru's long-term vision.
2
1
9
212
Yonatan retweeted

Today we're launching @tryAlanAI so developers can stop babysitting their coding agents.
We kept running into the same problem ourselves.
Even as agents got better at writing code, we were becoming glorified button-pushers for our own AI: starting every run, feeding them lures, and checking their work.
We built Alan to change that.
We kept running into the same problem ourselves.
Even as agents got better at writing code, we were becoming glorified button-pushers for our own AI: starting every run, feeding them lures, and checking their work.
We built Alan to change that.
242
112
611
210,103
Yonatan retweeted

Introducing Legend Spark!
It’s a React Native desktop framework for really fast desktop apps with React Native and Expo.
The biggest gaps in RN on desktop have been getting started, Expo compatibility, and modules. So I’m trying to fix all of that.
Let's make apps super fast!
It’s a React Native desktop framework for really fast desktop apps with React Native and Expo.
The biggest gaps in RN on desktop have been getting started, Expo compatibility, and modules. So I’m trying to fix all of that.
Let's make apps super fast!
43
58
564
20,031
📣 Tune in for #LoFi/42 on Tuesday at 8 AM PDT (October 27).
1️⃣ Steven @liechti_dev: Rust, iroh and CRDTs in a native workspace
2️⃣ Kushagar @KushagarGoel: Bring local-first to your backend
3️⃣ Schalk Venter: Local-first without the commitment
🧵👇
1️⃣ Steven @liechti_dev: Rust, iroh and CRDTs in a native workspace
2️⃣ Kushagar @KushagarGoel: Bring local-first to your backend
3️⃣ Schalk Venter: Local-first without the commitment
🧵👇

1
1
7
438
These meetups are made possible by our wonderful sponsors:
jazz.tools/?utm_source=lo…
iroh.computer/?utm_source=lo…
vella.ai/?utm_source=lo…
jazz.tools/?utm_source=lo…
iroh.computer/?utm_source=lo…
vella.ai/?utm_source=lo…
0
0
0
32


What is going on right now?
#̢̛ͥ̀̽̽ͨ̌̓͆̇̀̽ͦͨͫͯ̏̎̇̈̚͜҉̕͢͏͡҉̸̶̛͢͡҉̵̨̭̳̘̹̫͔͖̜̠͖̫̲̖̱̤̻̖͉͢͞͡ͅͅ͏̸̷̢͑̊̀̐ͣͭͭ̉͂ͨ̽͒̊̎͛ͪ̊̎ͩͧ̀͝͠͠͏̸̵̵̷̵
#̢̛ͥ̀̽̽ͨ̌̓͆̇̀̽ͦͨͫͯ̏̎̇̈̚͜҉̕͢͏͡҉̸̶̛͢͡҉̵̨̭̳̘̹̫͔͖̜̠͖̫̲̖̱̤̻̖͉͢͞͡ͅͅ͏̸̷̢͑̊̀̐ͣͭͭ̉͂ͨ̽͒̊̎͛ͪ̊̎ͩͧ̀͝͠͠͏̸̵̵̷̵
3
0
0
168
Two critical vulnerabilities have been identified in PHP, a widely used programming language that powers websites and web applications. These vulnerabilities (CVE-2026-109618 and CVE-2026-109619) could allow malicious cyber actors to remotely execute code in PHP core, potentially data and networks.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on php.net. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or ic3.gov. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information, follow PHP’s announcement on php.net, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.


0
0
0
30
😱
This is the most serious 48 hours in cybersecurity history.
"Black October" they're calling it
It seems every *hour* there's a new incident, that in a typical year, would be one of the biggest incidents of the *entire year*
SUMMARY OF THE LAST 48 HOURS:
YEAR-LEVEL INCIDENTS se would be among the biggest incidents of the year):
1. PHP2Shell: a hole in the software behind ~70% of websites. Governments took sites offline.
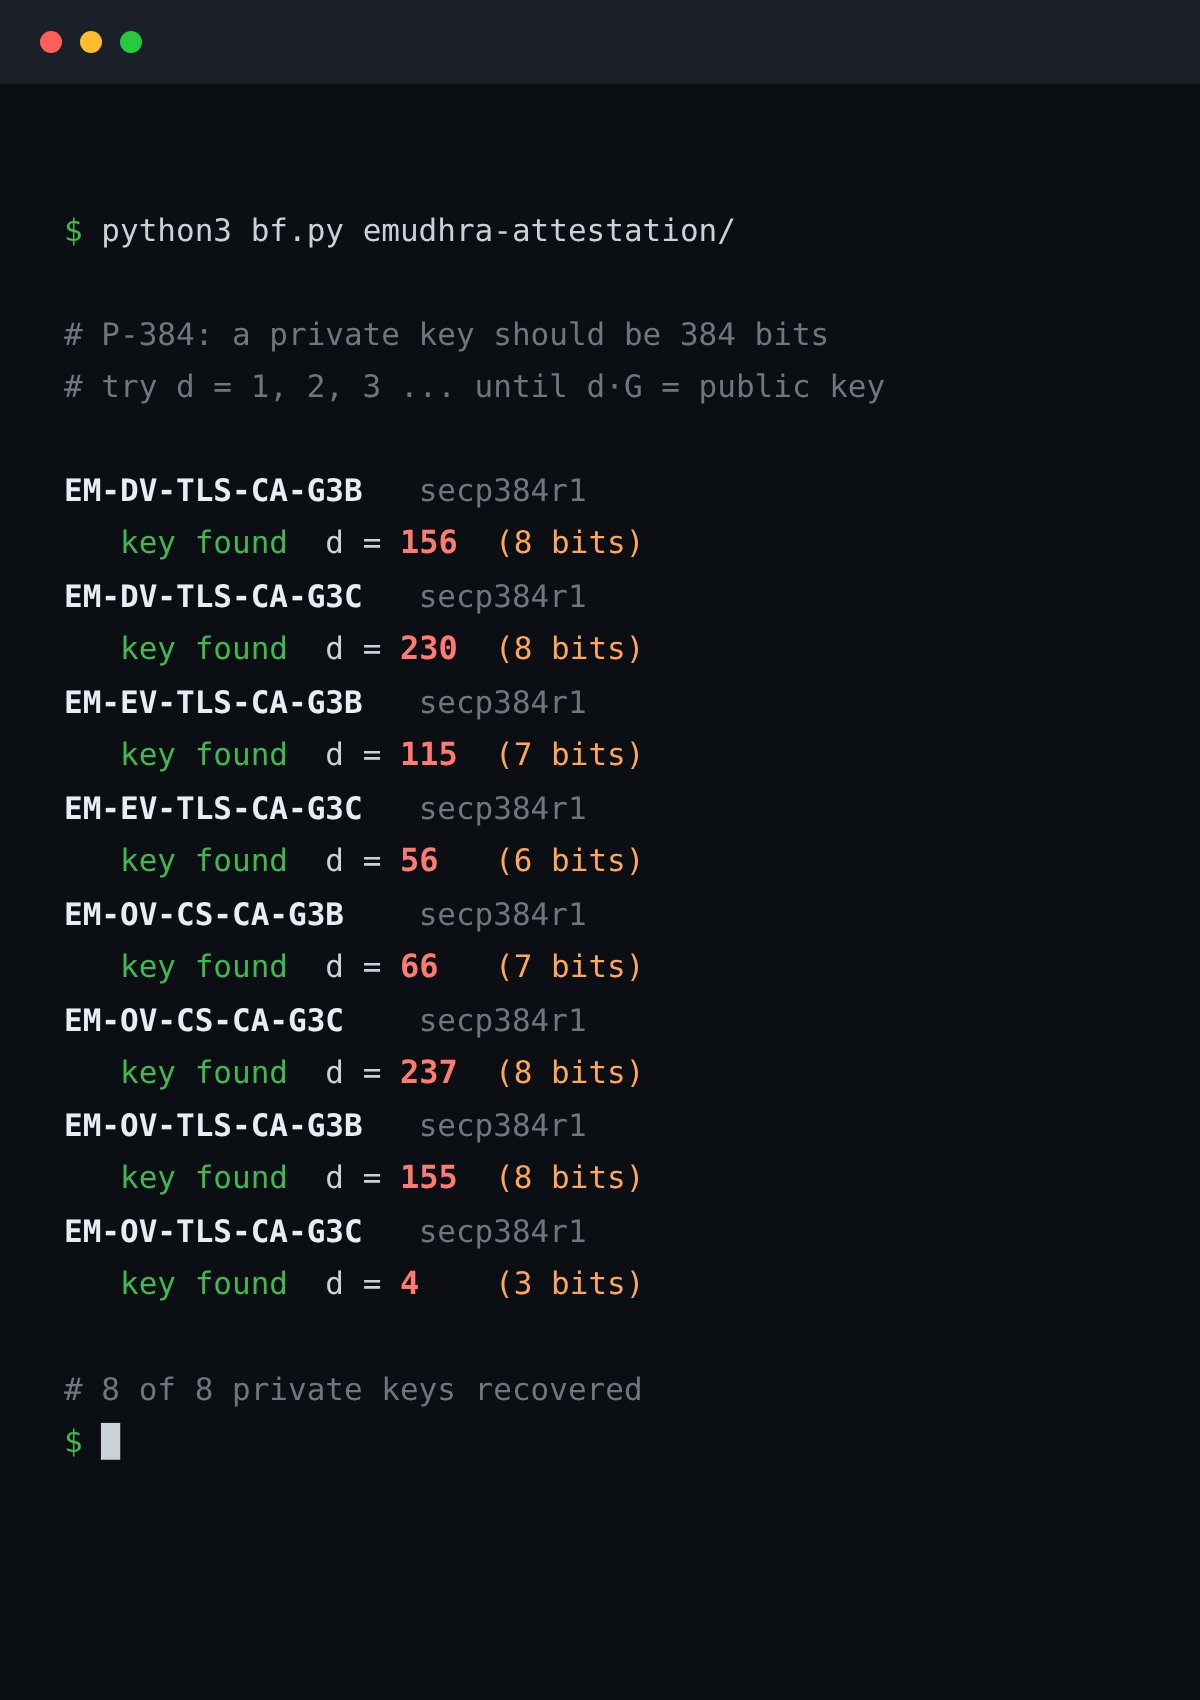
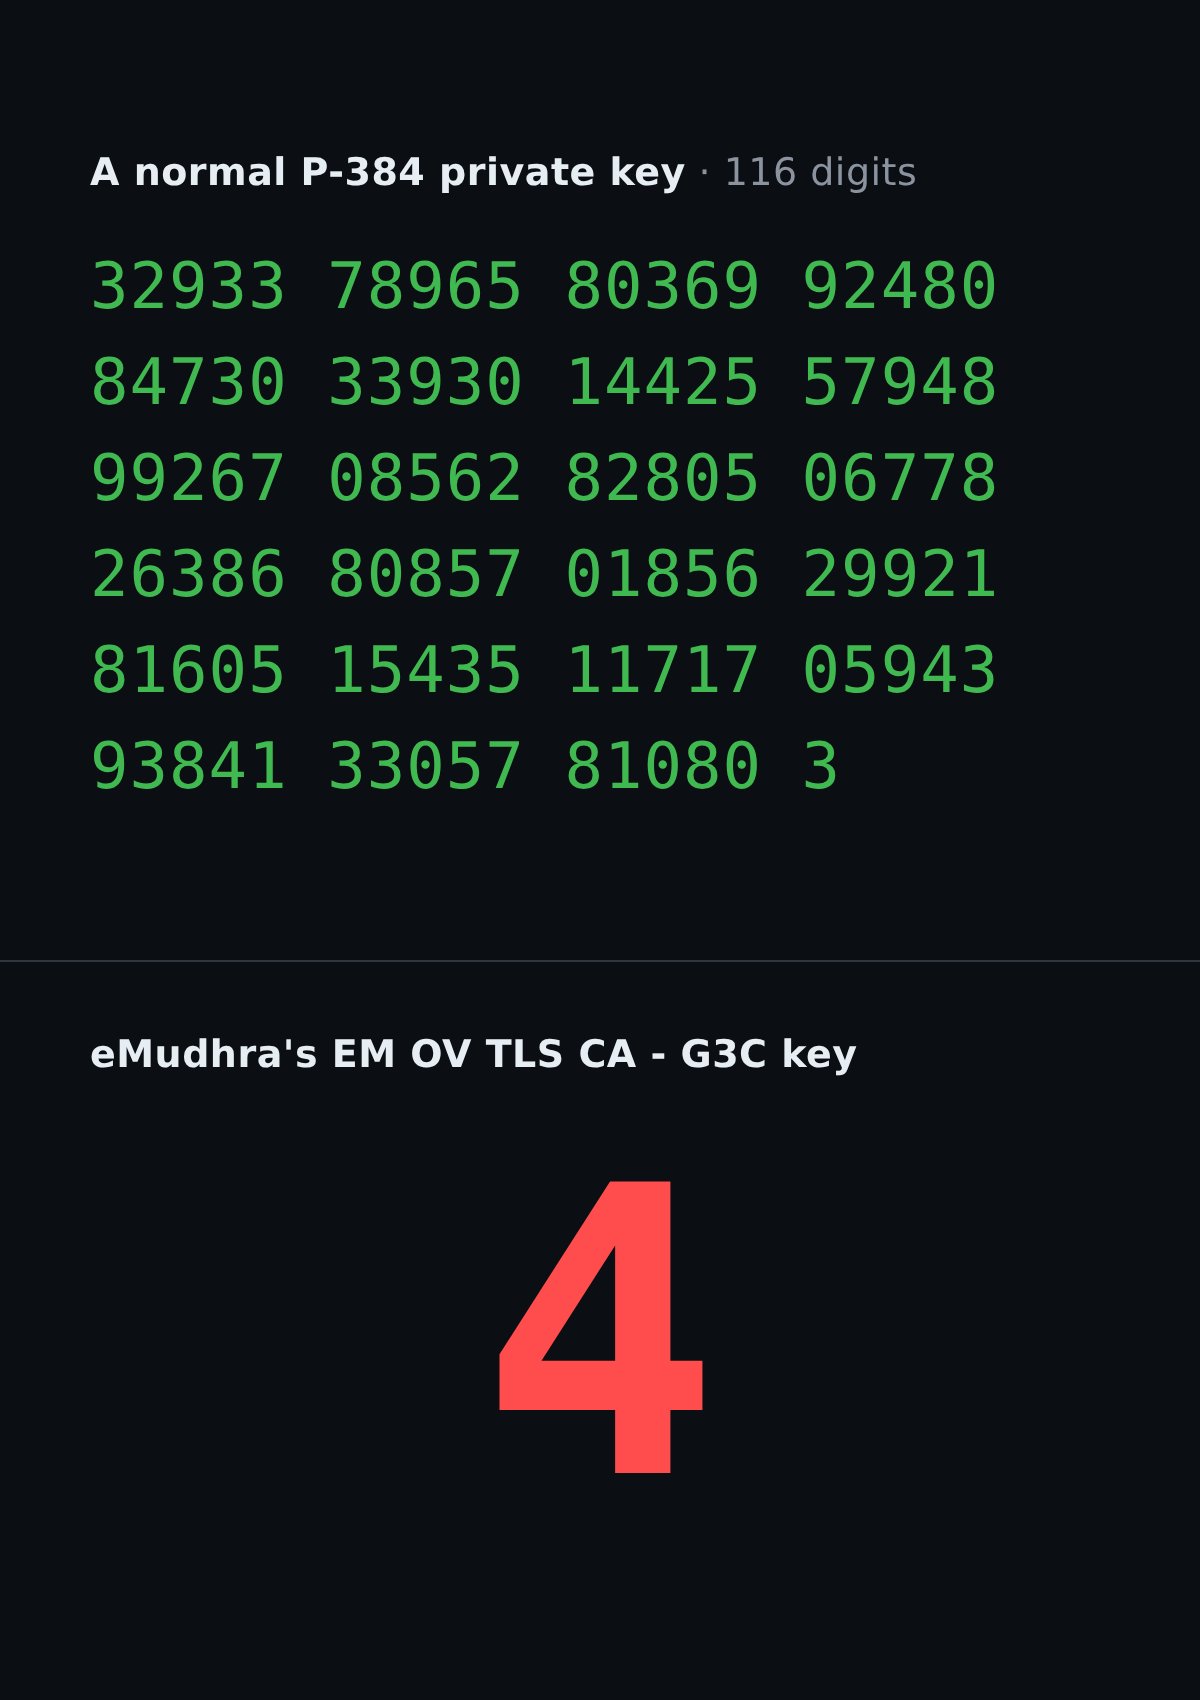
2. eMudhra: the master keys that prove websites are real were cracked. One was the number 4.
3. California: data on every public school student since 2023 stolen, including disability status
4. Railway: hackers stole customers' secret keys from a hosting platform used by millions of developers
5. Zeabur: 321,810 accounts breached. The company is shutting down.
6. LiteLLM: an AI tool downloaded 3.4 million times a day was poisoned with a password stealer
7. GitLab: a 10-out-of-10 severity hole in every version since 2014
8. Cairn: criminals used an AI hacking tool to break into 100+ companies
9. Ahold Delhaize: hackers knocked the owner of Food Lion and Stop & Shop offline
10. Onamae: malware planted on up to 26,739 customer servers in Japan
MONTH-LEVEL INCIDENTS (In a typical month, these would be among the biggest incidents):
11. Signal: a bug could leave your mic and camera on after you hang up
12. NGINX: 3 critical holes in software running ~1/3 of websites
13. HTTP/3: a single connection can crash 7 of the 10 web server types tested
14. Plex: hackers breaking into home media servers
15. SafePay ransomware: FBI warns it has hit 600+ critical infrastructure organizations
16. Palo Alto: ransomware gangs breaking in through company firewalls
17. Bullhorn: platform used by 10,000+ companies knocked offline
18. Medi-Cal: 970,000 patients' data stolen
19. WordPress: hackers stole a plugin maker's keys and used them to plant backdoors on websites
20. AOMEI: backup software's update server handed out a backdoor
21. Meta Muse: Meta's AI agent exposed users' personal and business secrets
22. Tor: 333 relays hijacked to steal logins
23. TiDB Cloud: database company's cloud breached
Also serious:
24. State Bank of India: India's biggest bank confirms a data breach
25. OVHcloud: hackers slipped a password stealer into a cloud company's official tool
26. Siemens: a software hole being used to spread malware
27. North Korea: state hackers launch a new attack campaign on South Korea

2
0
0
72
😱
This is the most serious 48 hours in cybersecurity history.
"Black October" they're calling it
It seems every *hour* there's a new incident, that in a typical year, would be one of the biggest incidents of the *entire year*
SUMMARY OF THE LAST 48 HOURS:
YEAR-LEVEL INCIDENTS se would be among the biggest incidents of the year):
1. PHP2Shell: a hole in the software behind ~70% of websites. Governments took sites offline.
2. eMudhra: the master keys that prove websites are real were cracked. One was the number 4.
3. California: data on every public school student since 2023 stolen, including disability status
4. Railway: hackers stole customers' secret keys from a hosting platform used by millions of developers
5. Zeabur: 321,810 accounts breached. The company is shutting down.
6. LiteLLM: an AI tool downloaded 3.4 million times a day was poisoned with a password stealer
7. GitLab: a 10-out-of-10 severity hole in every version since 2014
8. Cairn: criminals used an AI hacking tool to break into 100+ companies
9. Ahold Delhaize: hackers knocked the owner of Food Lion and Stop & Shop offline
10. Onamae: malware planted on up to 26,739 customer servers in Japan
MONTH-LEVEL INCIDENTS (In a typical month, these would be among the biggest incidents):
11. Signal: a bug could leave your mic and camera on after you hang up
12. NGINX: 3 critical holes in software running ~1/3 of websites
13. HTTP/3: a single connection can crash 7 of the 10 web server types tested
14. Plex: hackers breaking into home media servers
15. SafePay ransomware: FBI warns it has hit 600+ critical infrastructure organizations
16. Palo Alto: ransomware gangs breaking in through company firewalls
17. Bullhorn: platform used by 10,000+ companies knocked offline
18. Medi-Cal: 970,000 patients' data stolen
19. WordPress: hackers stole a plugin maker's keys and used them to plant backdoors on websites
20. AOMEI: backup software's update server handed out a backdoor
21. Meta Muse: Meta's AI agent exposed users' personal and business secrets
22. Tor: 333 relays hijacked to steal logins
23. TiDB Cloud: database company's cloud breached
Also serious:
24. State Bank of India: India's biggest bank confirms a data breach
25. OVHcloud: hackers slipped a password stealer into a cloud company's official tool
26. Siemens: a software hole being used to spread malware
27. North Korea: state hackers launch a new attack campaign on South Korea
0
0
0
13
who's got underdog invites? I'd like one @underdogai
I want to see if it can outshine developers.google.com/edge/foresight
I want to see if it can outshine developers.google.com/edge/foresight
1
0
4
178